What Is a Compliance Matrix? Meaning + 7-Step Build Process
Learn what a compliance matrix is, why proposal teams use one, how to build it, common mistakes to avoid, and where AI fits into modern RFP compliance workflows.
In 2015, 16 of 18 vendors bidding on a GSA Alliant Small Business IT services contract for USDA's National Information Technology Center were ruled technically unacceptable. The disqualifications were not about weak solutions. They were about proposals that omitted required information or took exception to the solicitation. Every one of those vendors spent weeks writing a losing proposal. A compliance matrix would have caught the gaps in a fraction of the time.
This guide covers what belongs in a compliance matrix, how to build one step by step, how federal and commercial matrices differ, common mistakes to avoid, and when to move from spreadsheets to AI-powered tools.
TL;DR
- A compliance matrix maps every RFP requirement to the response that addresses it, with columns for owner, status, and proposal location.
- Federal RFPs often require a specific matrix format tied to Section L and Section M. Commercial RFPs leave the format to the vendor.
- The seven-step build process: check for a required format, extract every requirement, categorize by type, assign one owner per row, link to proposal sections, update on amendments, final review before submission.
- Most compliance failures come from paraphrased requirements, missed amendments, and shared ownership. One row, one owner, exact wording.
- Spreadsheets work for small RFPs. AI compliance matrix tools take over once you're responding to 100+ requirement RFPs with multiple contributors.
What is a compliance matrix?
A compliance matrix, also called a proposal compliance matrix, RFP compliance matrix, or bid compliance matrix, is a document that maps every requirement in an RFP to the exact place it’s addressed in your proposal. It helps proposal teams verify that every instruction has been answered before submission and gives evaluators a faster way to review compliance.
You'll hear a few related terms used alongside it. A cross-reference matrix shows evaluators where each requirement is answered. An RFP shred is the raw list of every requirement pulled out of the solicitation, copied word-for-word. A compliance matrix builds on both. It captures each requirement, links it to your response, and tracks whether that requirement is met, fully, partially, or not at all.
For smaller opportunities, a checklist may be enough. But as RFPs grow more complex and involve multiple contributors, a compliance matrix becomes the central source of truth for tracking requirements, assigning ownership, and verifying compliance.
Why compliance matrices exist
A compliance matrix exists for one reason: to make sure no requirement is overlooked.
Before evaluators assess your technical approach or pricing, they first verify that your proposal follows the buyer's instructions. Missing a mandatory requirement can lead to clarification requests, lower evaluation scores, or outright disqualification.
Modern RFPs make compliance more challenging because requirements are often spread across the main solicitation, statements of work (SOWs), pricing schedules, security questionnaires, appendices, and amendments. Keeping track of these documents manually becomes increasingly difficult as opportunities grow.
A compliance matrix solves that problem by helping proposal teams:
- Capture every requirement
- Assign ownership
- Track completion
- Link each requirement to its proposal location
- Verify compliance before submission
It also improves the review experience for buyers by making it easier to verify where each requirement has been addressed.
Many proposal teams build the first version of the compliance matrix during the bid/no-bid stage. This helps identify mandatory certifications, contract clauses, submission requirements, and resource commitments before investing significant time in proposal development.
Who uses compliance matrices?
Compliance matrices are commonly used by:
- Proposal managers
- Capture managers
- Sales engineering teams
- Solution consultants
- Government contractors
- Enterprise sales teams
- Bid management teams
Any team responding to complex RFPs can benefit from a structured approach to tracking requirements.
The real cost of non-compliance
A non-compliant proposal does more than lose one deal. It compounds in four ways:
- Wasted response hours: Teams can spend 40 to 80 hours building a proposal that gets eliminated for a missing certification or unmet mandatory requirement. A compliance matrix catches those gaps before drafting begins.
- Evaluator confidence loss: Small gaps can make reviewers question the entire response. In competitive deals, that doubt can affect technical and pricing scores even when those sections are strong.
- Repeated losses on the same requirement: When the same requirement repeatedly causes non-compliance across tenders, it may signal a product, security, or process gap worth fixing. A compliance matrix makes these patterns visible.
- Revenue protection, not admin: Every unanswered mandatory requirement puts the entire deal at risk. Compliance tracking is a revenue function, not just an administrative task.
Core components of a compliance matrix
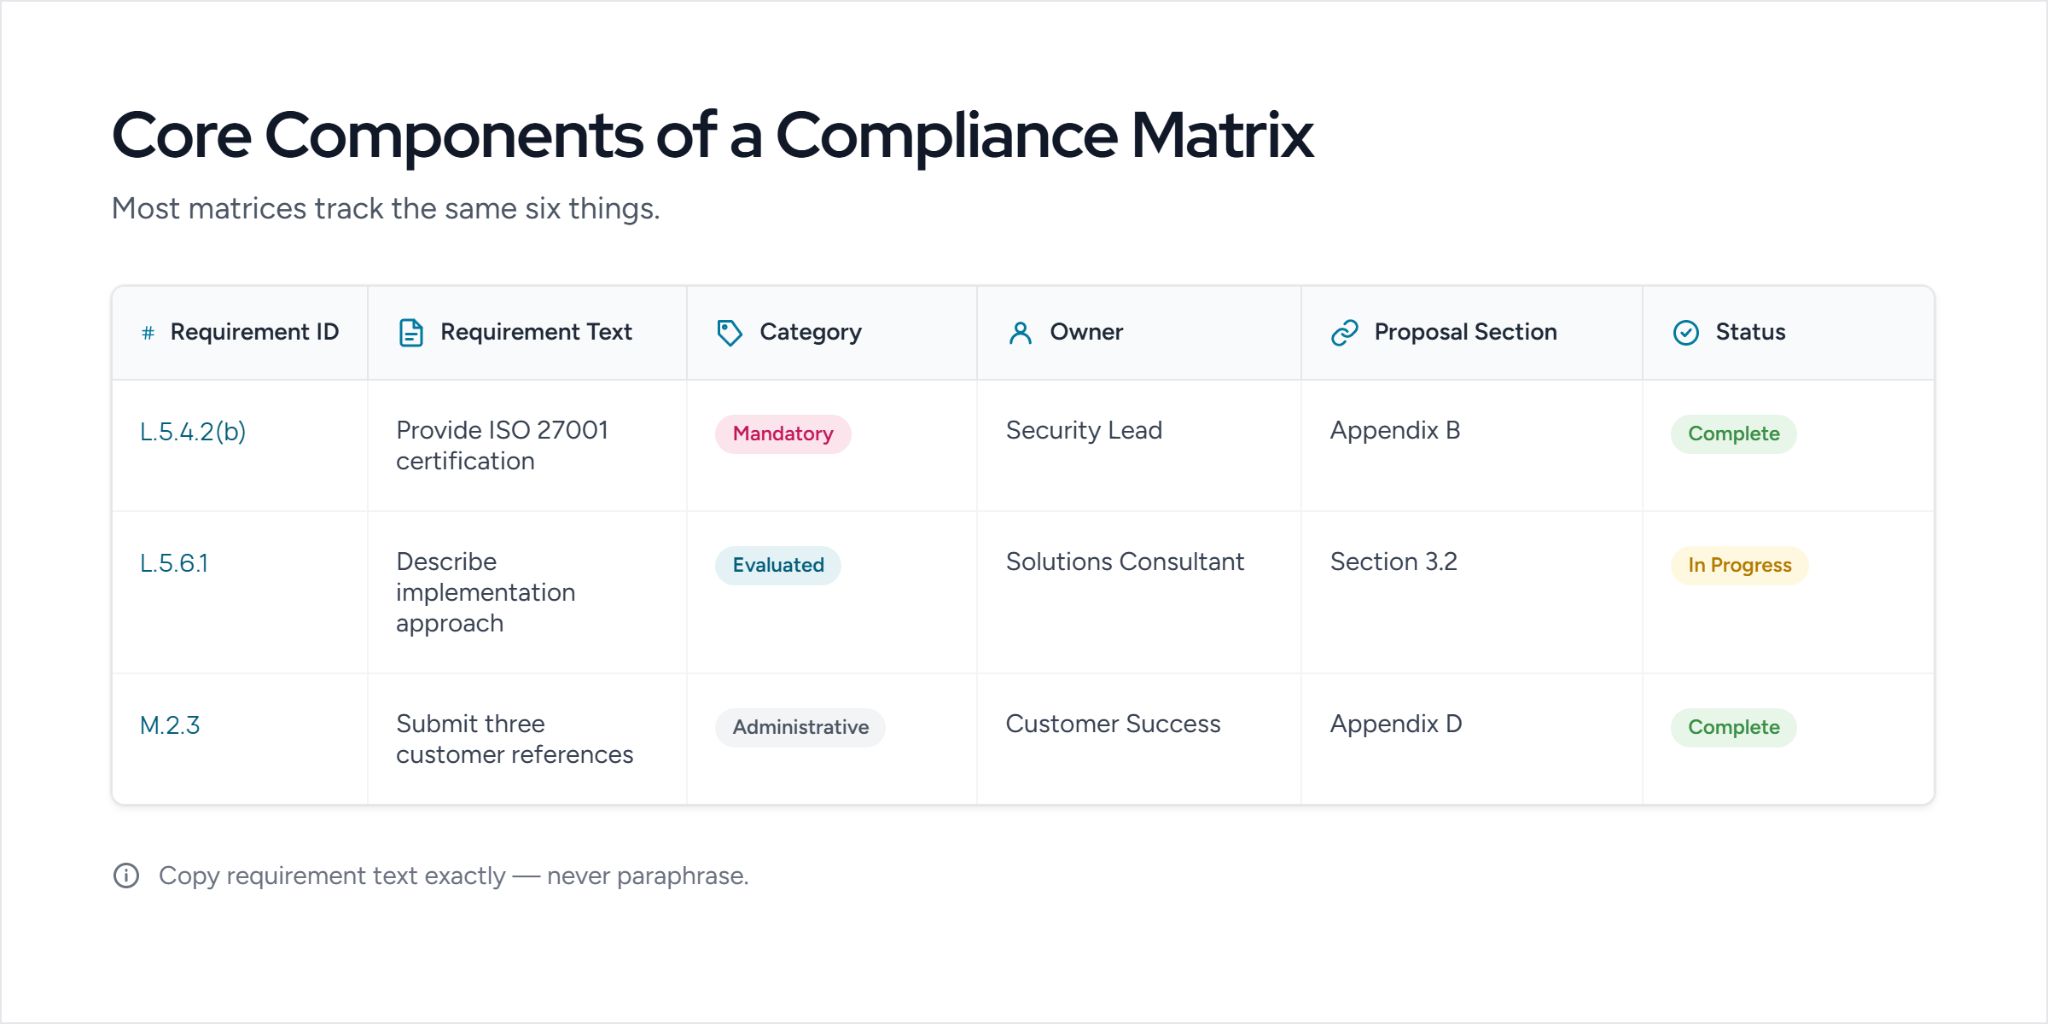
Although formats vary between organizations, most compliance matrices include the same core information.
The most important rule for a compliance matrix is simple: Copy requirement text exactly as written.
Paraphrasing can unintentionally change the meaning of a requirement or combine multiple instructions into one. Keeping the original language makes reviews easier and reduces the chance of missing important details.
Requirement types explained
Not every requirement carries the same weight. Categorizing them early helps teams prioritize their work.
Pay close attention to administrative requirements. While teams often focus on technical responses, simple issues like missing signatures, incorrect file names, or page-limit violations can create avoidable compliance problems.
Compliance matrix example
Many teams start with an Excel compliance matrix template before moving to proposal management software as RFP complexity grows.
For filled-out examples across government, SaaS, healthcare, and other industries, see our template guide.
Compliance matrix vs requirements traceability matrix
A compliance matrix and a requirements traceability matrix (RTM) describe the same artifact: a table that maps requirements to the responses or implementations addressing them. "Compliance matrix" is the government-proposal and bid response term. "Requirements traceability matrix" is the systems-engineering term for the same tool, used in product development, software engineering, and project management.
The structure is the same (requirement, source, owner, status, response or implementation location), but the usage differs. A compliance matrix tracks a vendor's response to a buyer's RFP. An RTM tracks a product team's implementation against a specification. In government proposal work, the two terms are often used interchangeably.
Federal vs. commercial compliance matrices
A compliance matrix serves the same purpose across procurements, but how you build one depends on the buyer.
Federal compliance matrices
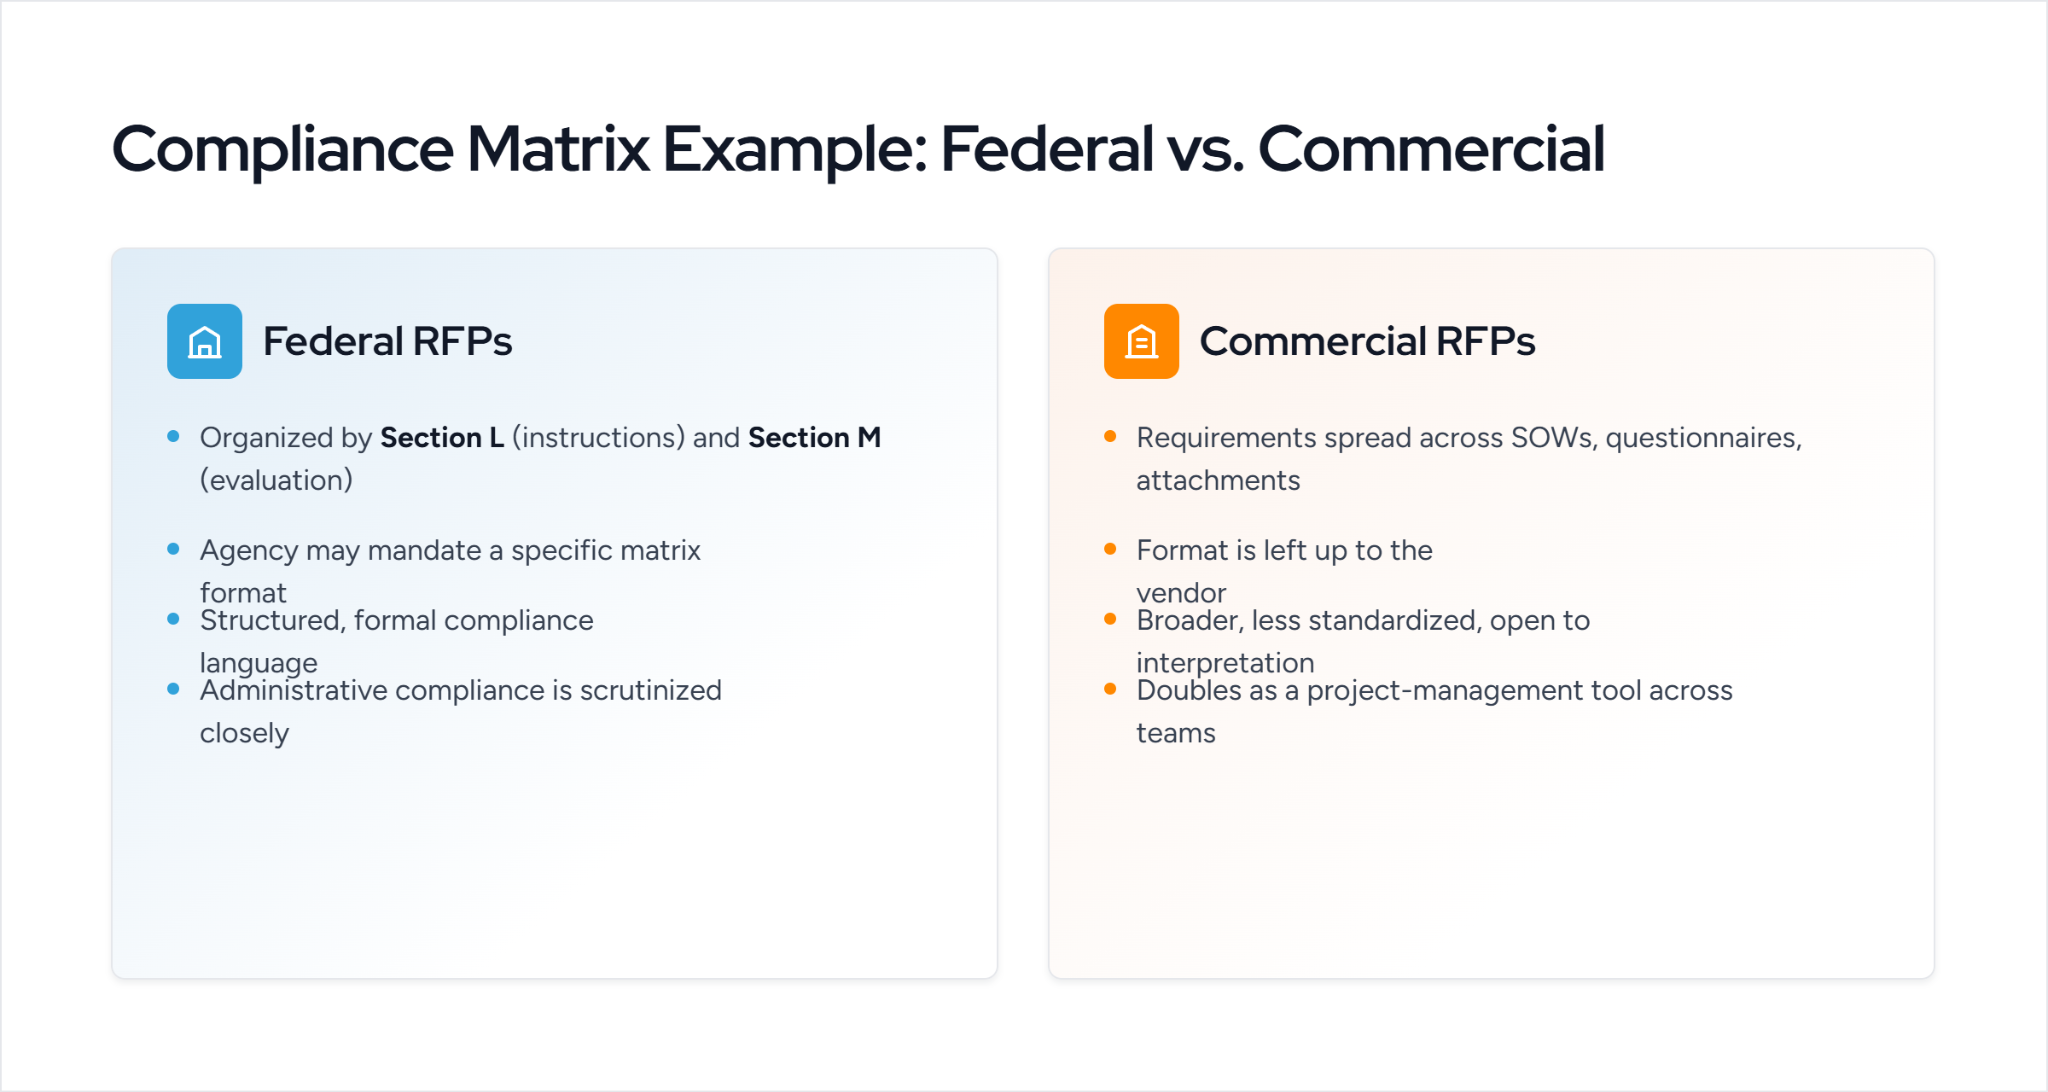
Federal solicitations often separate proposal instructions from evaluation criteria.
- Section L explains how the proposal should be prepared and submitted.
- Section M explains how evaluators will assess proposals.
Requirements may also appear in statements of work, contract clauses, attachments, pricing schedules, and amendments. Before creating your own template, check whether the agency provides one. If the solicitation specifies a format, use it.
Commercial compliance matrices
Commercial RFPs usually leave the format up to the vendor. The challenge is identifying requirements across statements of work, security questionnaires, pricing documents, appendices, email clarifications, and amendments.
Because commercial RFPs often involve contributors from sales, product, security, legal, finance, and customer success, a compliance matrix also serves as a project management tool. It clarifies ownership, tracks progress, and helps identify gaps before submission.
Commercial buyers may never ask to see your compliance matrix, but maintaining one internally reduces review cycles and simplifies final compliance checks.
How to build a compliance matrix
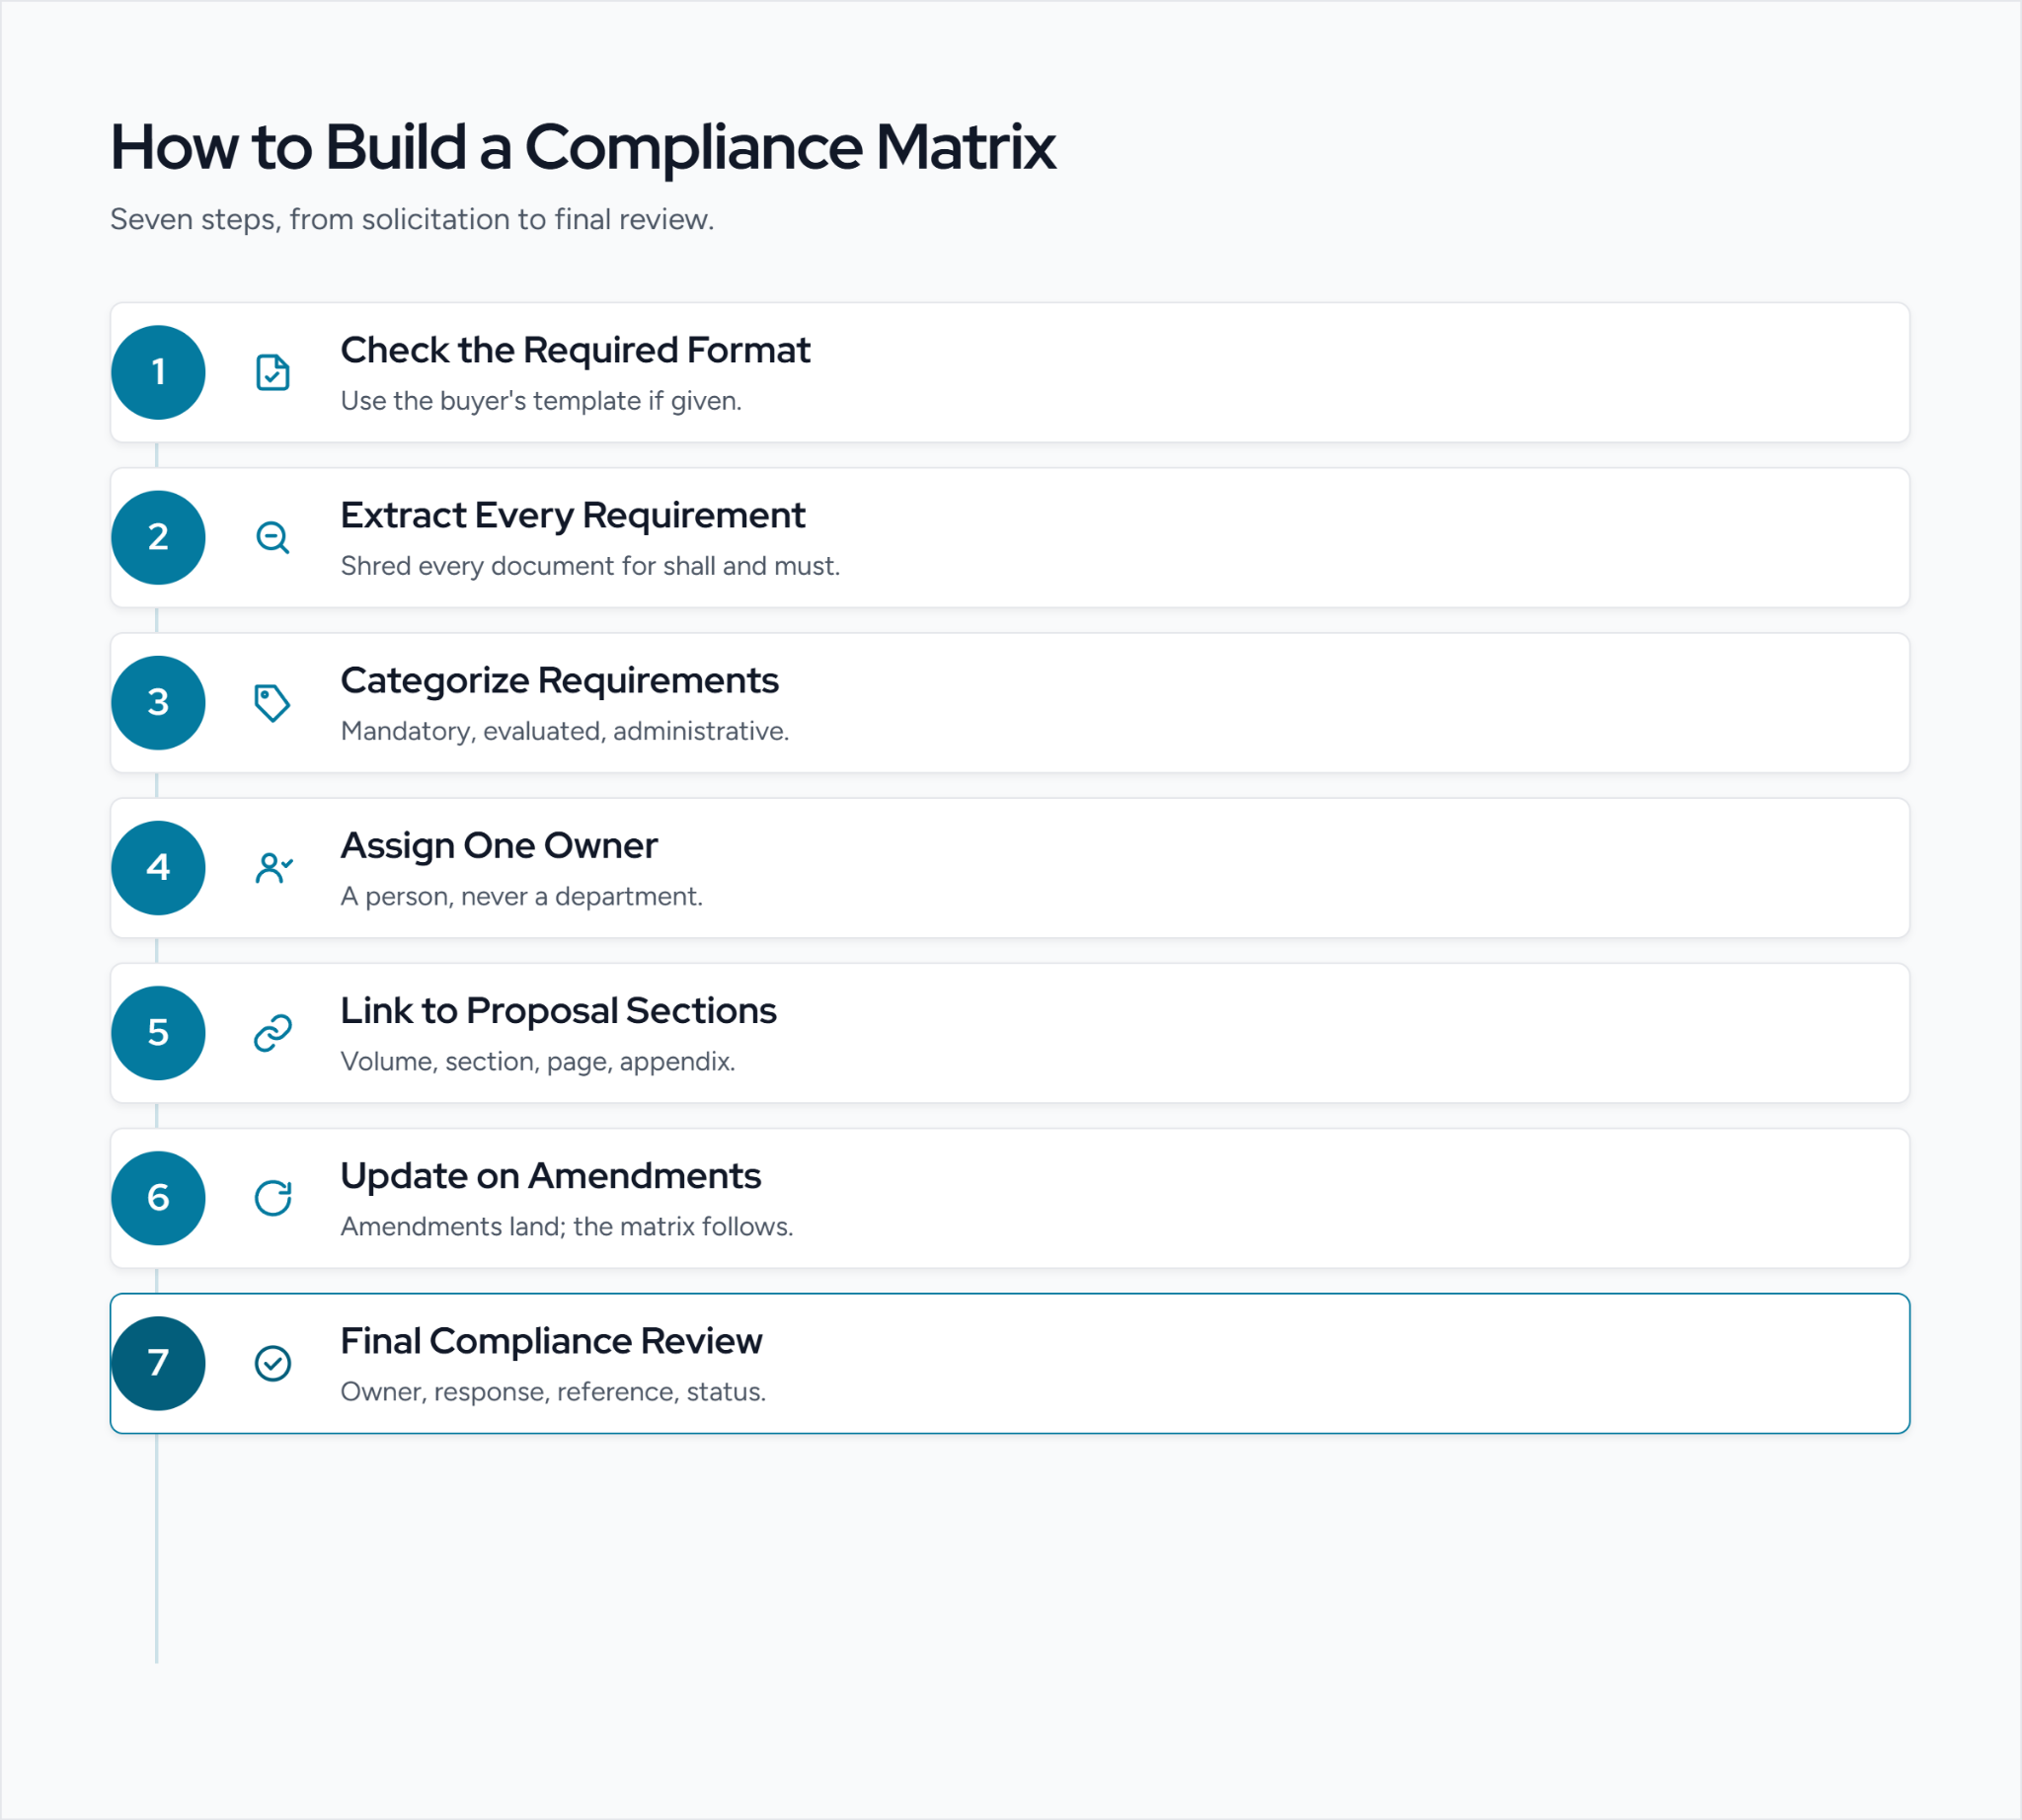
A compliance matrix is only valuable if it's complete and stays up to date throughout the proposal process. Whether you're using a spreadsheet or proposal software, the fundamentals remain the same.
Build the matrix first, not last
The most common compliance failure is treating the matrix as a final review step. By then, the proposal is already written, mapping requirements back to the response is manual, and fixing gaps is expensive.
Build the matrix first:
- Extract requirements before anyone starts writing.
- Answer the RFP directly in the matrix columns.
- Generate the proposal document from the completed matrix.
- Use the matrix as the compliance check by reviewing the columns you have already filled.
This also changes the final two days before the deadline. Instead of rereading the entire proposal to find omissions, filter for:
- Rows with no answer
- Rows with no supporting evidence
- Rows marked partially compliant
Then focus the team on resolving that short list.
1. Check for a required format
Read the RFP before you design anything. Federal agencies sometimes provide a mandatory matrix template or dictate how requirements must be organized. Commercial buyers rarely do.
If the buyer specifies a format, use it exactly; a matrix that ignores the required structure can itself count as non-compliant. If no format is given, lock in your columns before you start extracting, so you're not restructuring halfway through.
2. Extract every requirement
This step decides whether the rest of the matrix holds up. Most disqualifications trace back to a requirement that was never captured.
Work through the solicitation line by line, a process proposal teams call RFP shredding. Pull every instruction, requirement, evaluation criterion, and submission rule before writing begins.
Look for explicit directive language:
- Shall
- Must
- Required
- Mandatory
Also capture softer directives. Words like describe, explain, demonstrate, provide, include, and list are still requirements. Be careful with "will" — in federal RFPs it often marks the government's own obligation, not something you must do.
Watch for compound requirements. A sentence that says "the vendor shall provide X and Y" is two requirements and belongs in two rows. Review every document tied to the opportunity, not just the main solicitation:
- Main RFP
- Statement of Work (SOW)
- Performance Work Statement (PWS)
- Pricing schedules
- Security questionnaires
- Appendices
- Attachments
- Amendments
- Buyer Q&A documents
Tip: Manual requirement extraction works well for smaller RFPs, but it becomes time-consuming when requirements are spread across multiple documents and amendments. AI-powered proposal platforms can help identify and organize requirements faster, though every extracted requirement should still be reviewed by a proposal manager.
3. Categorize each requirement
Classifying requirements early helps proposal managers prioritize work and identify compliance risks.
A practical approach is to label each requirement as:
- Mandatory: Failure to comply could result in disqualification.
- Evaluated: Contributes to proposal scoring.
- Administrative: Covers formatting, certifications, page limits, forms, and submission instructions.
- Informational: Requires supporting information or acknowledgment but isn't directly scored.
A requirement can fall into more than one category; a mandatory item is often evaluated too, so tag it for both. Handle mandatory and administrative requirements first: they carry the highest disqualification risk and are the easiest to overlook. Color-coding the categories makes large pursuits faster to review.
4. Assign one owner per requirement
Every requirement needs one named owner. Avoid assigning work to a department like Engineering or Legal; shared ownership usually means no one owns it.
The owner is accountable for the response, not necessarily the person who writes it. They can pull in SMEs, but they close the row. Assign owners right after extraction so contributors can work in parallel instead of waiting on one coordinator.
5. Link requirements to proposal sections
As proposal writing progresses, update the matrix with the exact location where each requirement is addressed.
Include:
- Proposal volume
- Section number
- Page number
- Supporting appendix or attachment, if applicable
Updating the matrix as you write makes final reviews easier and helps catch gaps before submission.
6. Update the matrix when requirements change
Treat the compliance matrix as a living document. If the buyer issues an amendment, clarification, or revised attachment, update the matrix immediately. Keeping it synchronized with the latest RFP documents reduces the risk of responding to outdated requirements.
7. Perform a final compliance review
Before submission, confirm that every requirement has an owner, a completed response, a proposal reference, and a clear compliance status.
On larger pursuits, this is formalized as a final review, often a Gold Team or white-glove check, that confirms what earlier reviews flagged is now resolved. Work through the matrix row by row; if any requirement lacks a response or reference, it gets fixed here.
If a requirement can't be fully met, document the rationale; don't delete the row. A clear, honest exception reads better to evaluators than a silent gap.
If you'd rather start from a working structure than build one from scratch, this compliance matrix template sets up these columns for you and includes editable examples you can adapt to your next RFP.
Key compliance matrix KPIs to track
Manual vs. spreadsheet vs. AI-powered compliance management
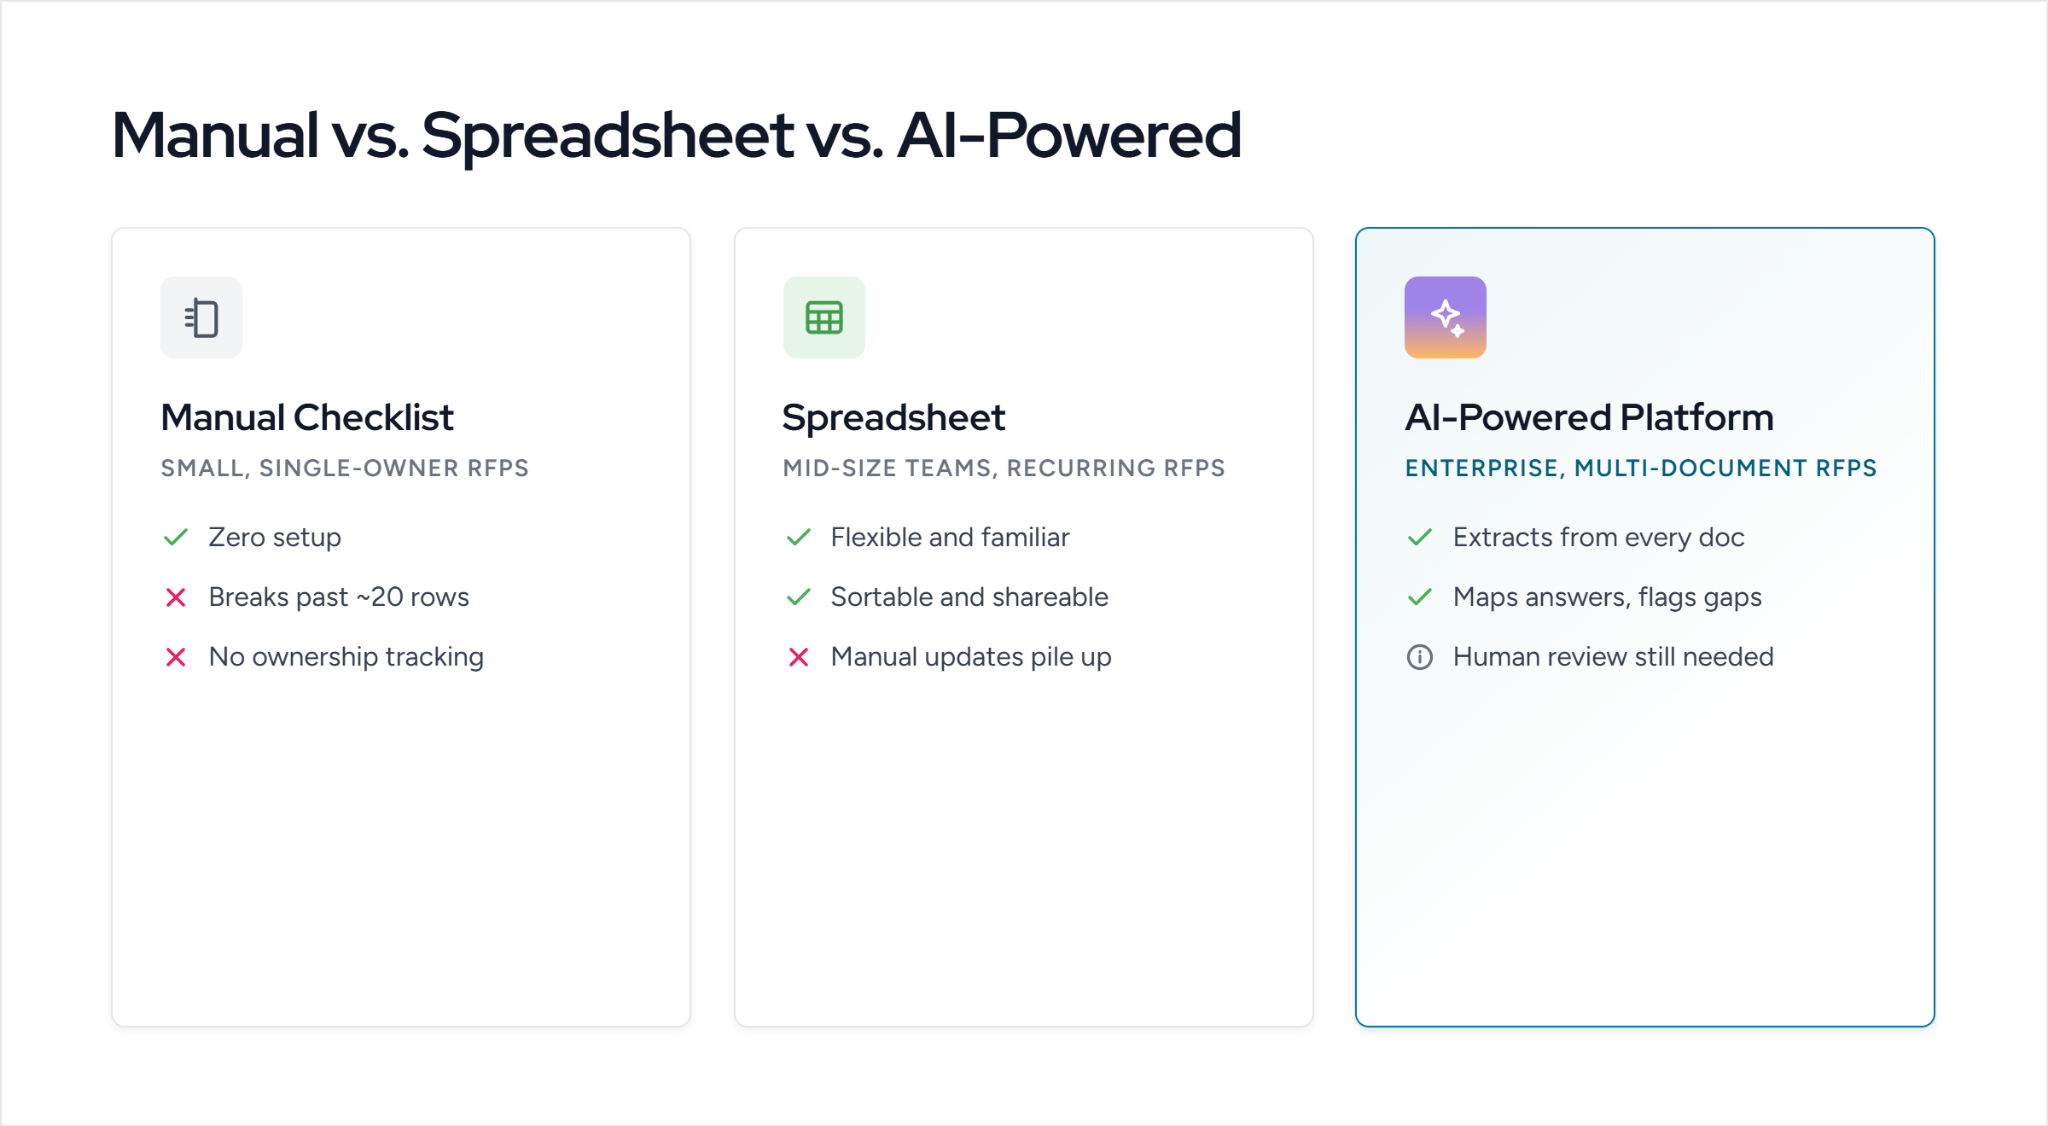
The best approach depends on your RFP complexity, proposal volume, team size, and collaboration needs.
Manual checklists
For short commercial questionnaires with only a handful of requirements, a formal compliance matrix may be unnecessary. A simple checklist or annotated copy of the RFP is often enough.
Spreadsheets
Spreadsheets remain the most common way to manage compliance matrices because they're flexible and easy to customize. As proposals grow, many teams adopt proposal management software to reduce manual updates and improve collaboration.
AI-powered proposal platforms
AI-powered proposal platforms reduce much of the manual work involved in responding to complex RFPs by helping teams move from requirement analysis to response drafting in a single workflow.
For example, Inventive AI helps proposal teams:
- Generate first drafts using connected knowledge sources instead of static content libraries
- Surface relevant proposals, certifications, security documentation, case studies, and approved answers
- Identify response gaps before formal reviews
- Keep responses consistent across contributors and business units
- Reduce time spent searching across multiple repositories
This is especially valuable for enterprise teams managing multiple RFPs at once, where finding the right content often takes longer than writing the response.
AI doesn't replace proposal management. Teams still need to verify extracted requirements, review buyer amendments, interpret ambiguous language, and confirm every response satisfies the RFP. Proposal teams use AI to reduce repetitive work while keeping compliance decisions under human oversight.
Common compliance matrix mistakes
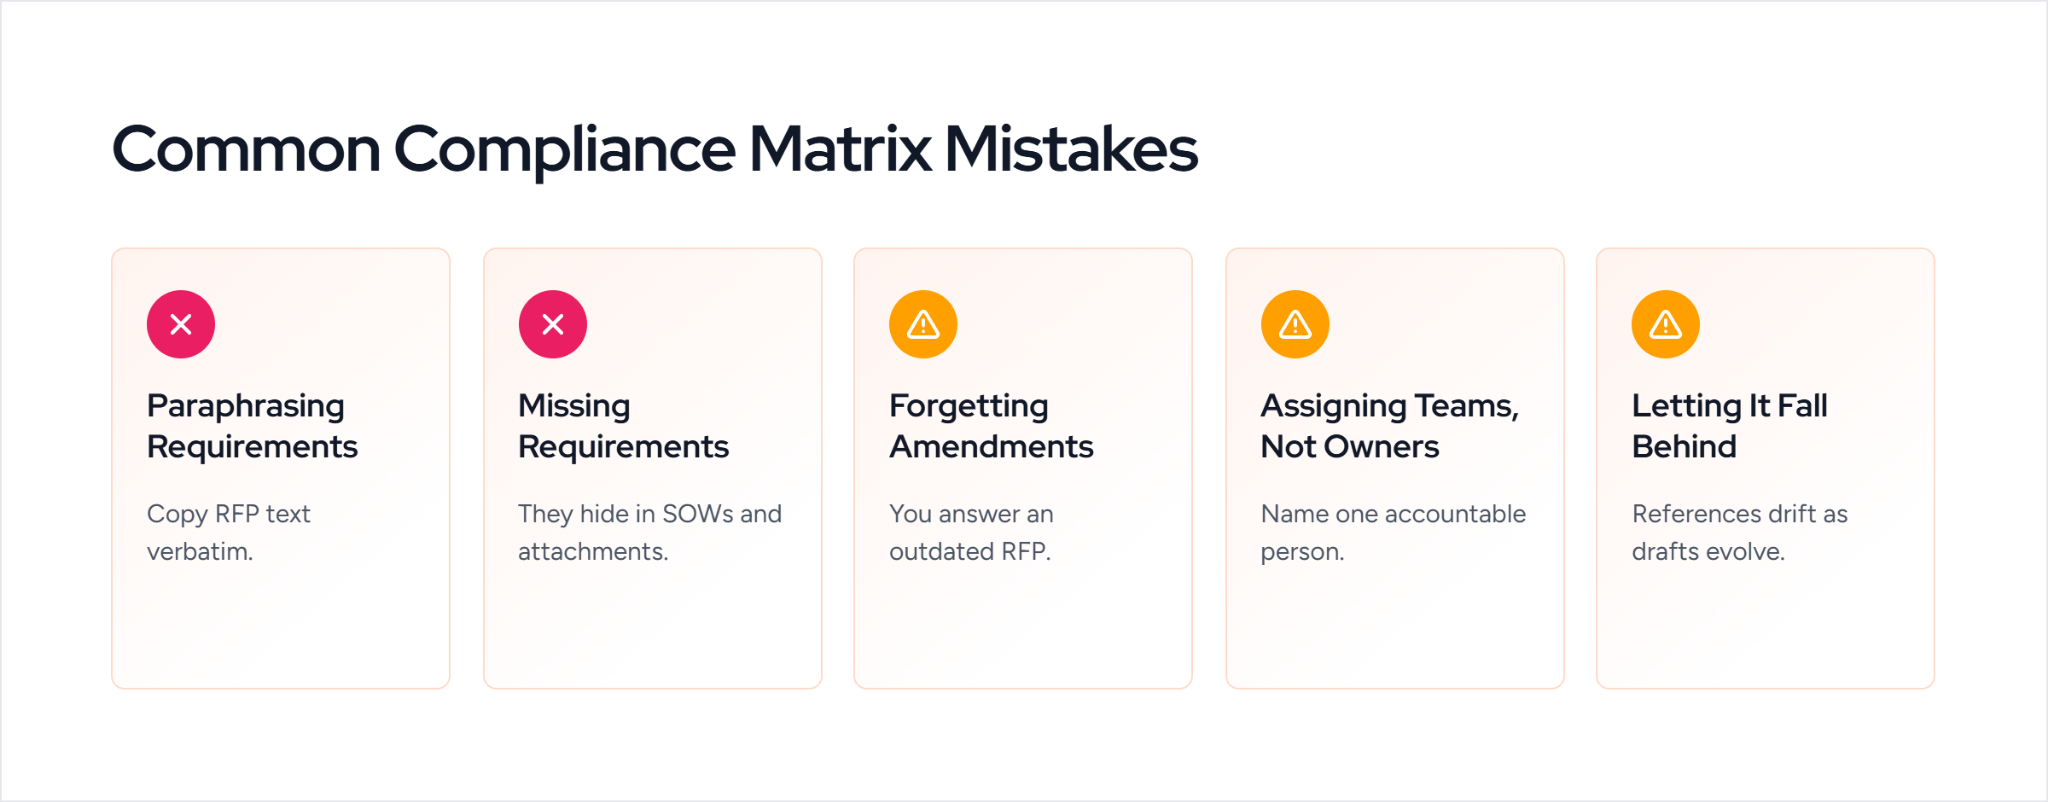
Even experienced proposal teams run into compliance issues. Most aren't caused by weak proposals. They happen because requirements aren't tracked consistently.
1. Paraphrasing requirements
Always copy requirement text exactly as it appears in the RFP. Rewording instructions can change their meaning or accidentally combine multiple requirements into one row.
2. Missing requirements across documents
Requirements rarely live in a single document. They can appear in statements of work, pricing schedules, attachments, security questionnaires, amendments, and buyer Q&A documents.
Before you start extracting, list every document tied to the opportunity. Work through each one, and repeat the check whenever a new file or amendment is released.
3. Forgetting amendments
Buyers often issue amendments after publishing an RFP. Amendments can change requirements, adjust page limits, move the due date, or add entirely new instructions.
The risk is working from an outdated version. You either respond to a requirement that no longer applies or miss one that was just added.
Log every amendment as it arrives and update the affected rows immediately. Note the amendment number in the matrix so reviewers can see the requirement reflects the latest version.
4. Assigning teams instead of owners
Assigning a requirement to "Engineering" or "Legal" feels efficient, but shared ownership usually means no ownership. Each person assumes someone else has it.
These are the requirements that slip near the deadline, when everyone is heads-down, and no one is clearly accountable.
Assign one named person to every requirement. That owner is responsible for the response, even if they pull in others to help. One row, one owner, one point of accountability.
5. Letting the matrix fall behind
Proposal sections move as drafts evolve. Content gets rewritten, sections get renumbered, and page references drift.
When the matrix isn't updated alongside the writing, the final review turns into a scramble. Gaps and mismatches surface late, when there's the least time to fix them.
Treat the matrix as a living document. Update status, section, and page references as you write, not in a rushed pass the night before submission.
Scale your compliance process with Inventive AI
Compliance matrix work has three expensive steps: reading the RFP, finding the right answer, and keeping both in sync as amendments land. Inventive AI collapses all three into one workflow.
Upload the RFP, SOW, and attachments. Inventive AI extracts every requirement into a compliance matrix with the source clause linked to each row. It then drafts a first response for each requirement by pulling from your connected knowledge sources, Google Drive, SharePoint, Confluence, Notion, Salesforce, and past proposals, so your SMEs review a draft instead of writing from scratch. When the buyer sends an amendment, the matrix updates in place.
The output is the same compliance matrix a proposal manager would build in a spreadsheet, except the extraction, drafting, and version control run on their own. That shift is what gets teams from one RFP a week to five without adding headcount.