SIG questionnaire guide: types, domains, and how to respond
What the SIG questionnaire is, SIG Core vs. SIG Lite, the 21 risk domains, example questions, licensing, the 2026 updates, and how to respond faster.
A SIG questionnaire can hold up an enterprise deal for weeks. It pulls in security, compliance, and legal, runs to hundreds of questions, and lands on your desk with a tight deadline.
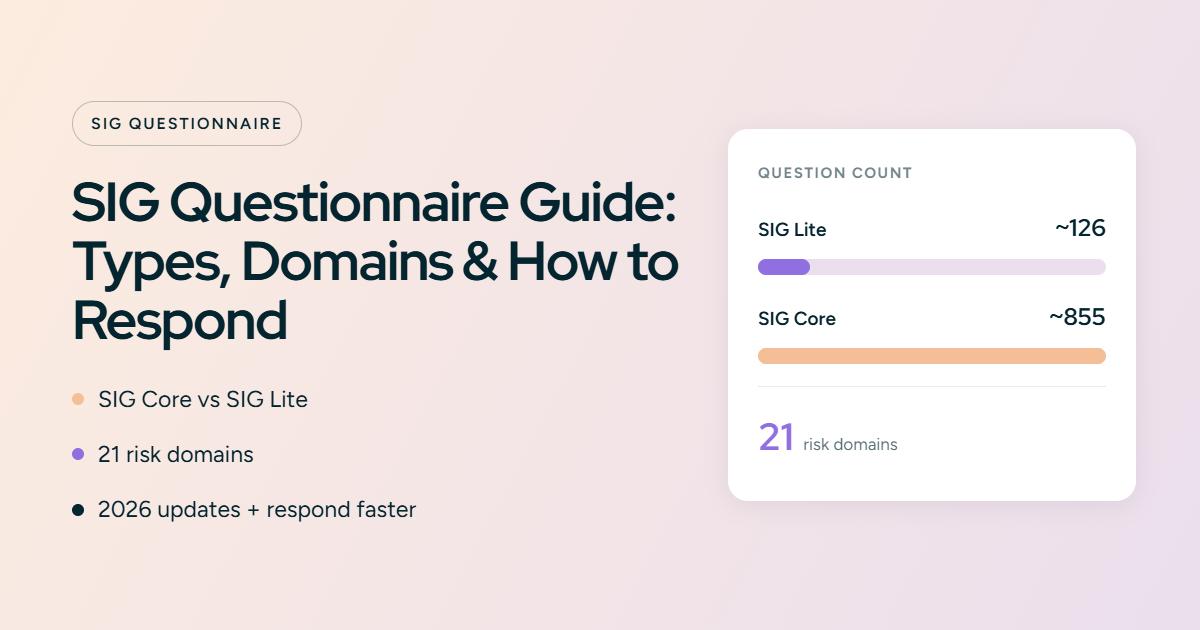
This guide explains what the SIG is, how SIG Core and SIG Lite differ, the 21 risk domains it covers, and how to respond to one faster, with the current 2026 updates included.
TL;DR
- The SIG (Standardized Information Gathering) questionnaire is a third-party risk assessment published by Shared Assessments, used by buyers to evaluate a vendor's security, privacy, and controls.
- Two main versions: SIG Lite (~126 questions) for a quick screen, and SIG Core (~855 questions across 21 risk domains) for high-risk vendors. Buyers can also send a customized SIG.
- It is licensed, not free. Shared Assessments members receive the SIG toolkit; the buyer typically sends you the version they want completed.
- It is updated yearly. Recent versions added AI and supply-chain (Nth party) domains; SIG 2026 adds ISO 42001 (AI governance) and operational-resilience mappings.
- The fastest way to respond is to reuse approved answers from past questionnaires and route only new questions to experts. Response software automates most of that reuse.
What is a SIG questionnaire?
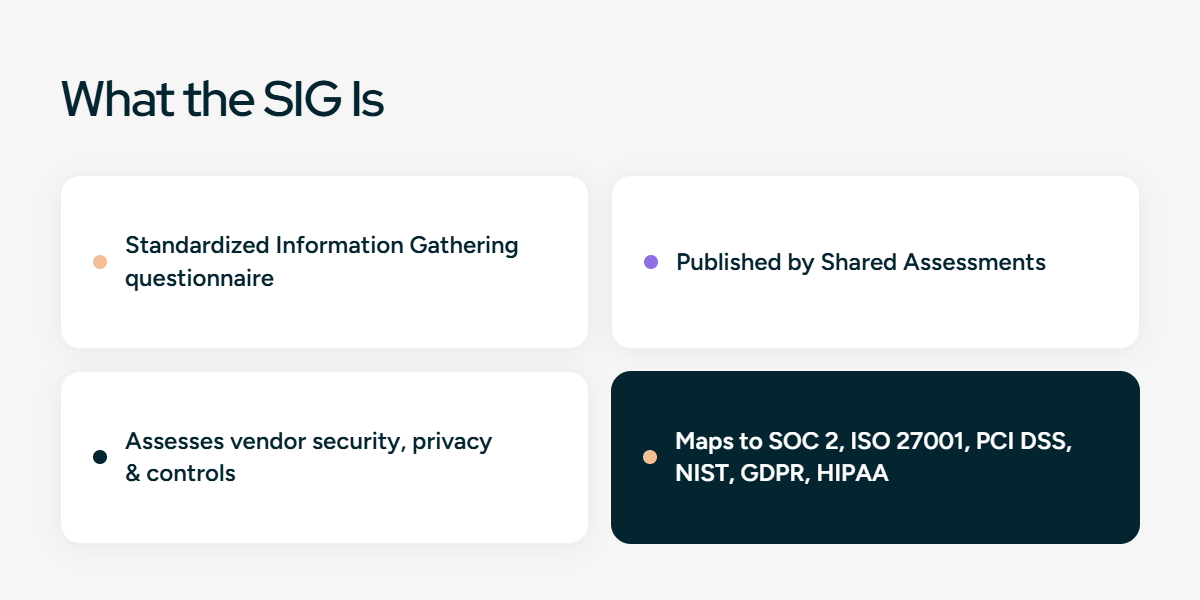
The SIG, or Standardized Information Gathering questionnaire, is a standardized set of questions that buyers use to assess the security and risk practices of a vendor before and during a relationship. It is published and maintained by Shared Assessments, a member organization that sets third-party risk management standards.
Because it is standardized, the SIG lets a buyer assess many vendors with one consistent framework, and it maps to widely used regulations and standards, including SOC 2, ISO 27001:2022, PCI DSS v4.0, NIST, GDPR, and HIPAA. For you as the vendor, that means one thorough questionnaire can satisfy several of a buyer's compliance requirements at once.
SIG Core vs. SIG Lite (and customized SIG)
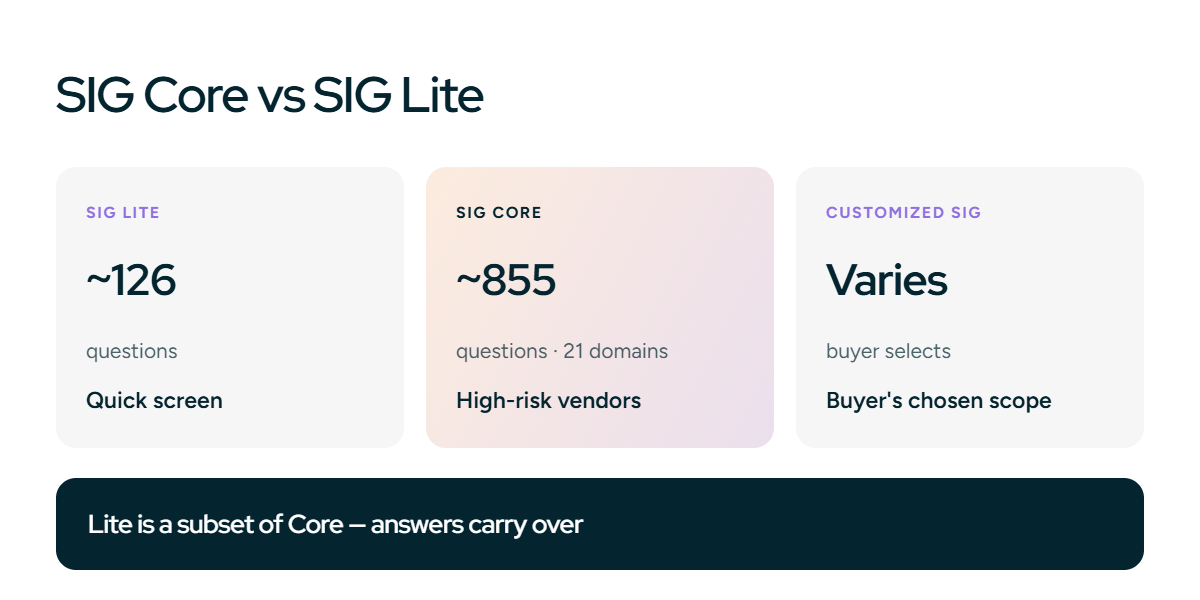
The SIG comes in scoping tiers so a buyer can right-size the assessment to the risk. The two standard versions are SIG Lite and SIG Core.
SIG Lite is a subset of SIG Core, so the answers you prepare for one carry over to the other. A buyer often starts with SIG Lite and follows up with SIG Core if the relationship involves sensitive data.
The 21 risk domains a SIG questionnaire covers
A full SIG is organized into 21 risk domains. Knowing them tells you which internal owners you will need and what evidence to have ready.
- Enterprise risk management
- Security policy and governance
- Human resources security
- Asset and information management
- Access control
- Application security
- Systems acquisition, development, and maintenance
- IT operations management
- Network security
- Endpoint security
- Server security
- Cloud hosting services
- Threat and vulnerability management
- Physical and environmental security
- Incident event and communications management
- Operational resilience and business continuity
- Compliance management
- Privacy management
- Training and awareness
- Artificial intelligence
- Supply chain (Nth party) risk management
Artificial intelligence and supply-chain (Nth party) risk are recent additions, reflecting how buyers now assess AI use and downstream vendor dependencies.
SIG questionnaire example questions
Questions are specific and evidence-based. A few representative examples, by domain:
- Access control: Is multi-factor authentication enforced for all remote and administrative access?
- Data and privacy: How is customer data encrypted at rest and in transit, and which algorithms are used?
- Incident management: What is your incident response process, and what is your breach notification timeline?
- Compliance: Do you hold SOC 2 Type II or ISO 27001 certification, and when was it last renewed?
- Supply chain: How do you assess and monitor the security of your own subcontractors and fourth parties?
Most questions expect a yes/no or short answer plus supporting evidence, such as a policy document or an audit report.
Why buyers use SIG questionnaires
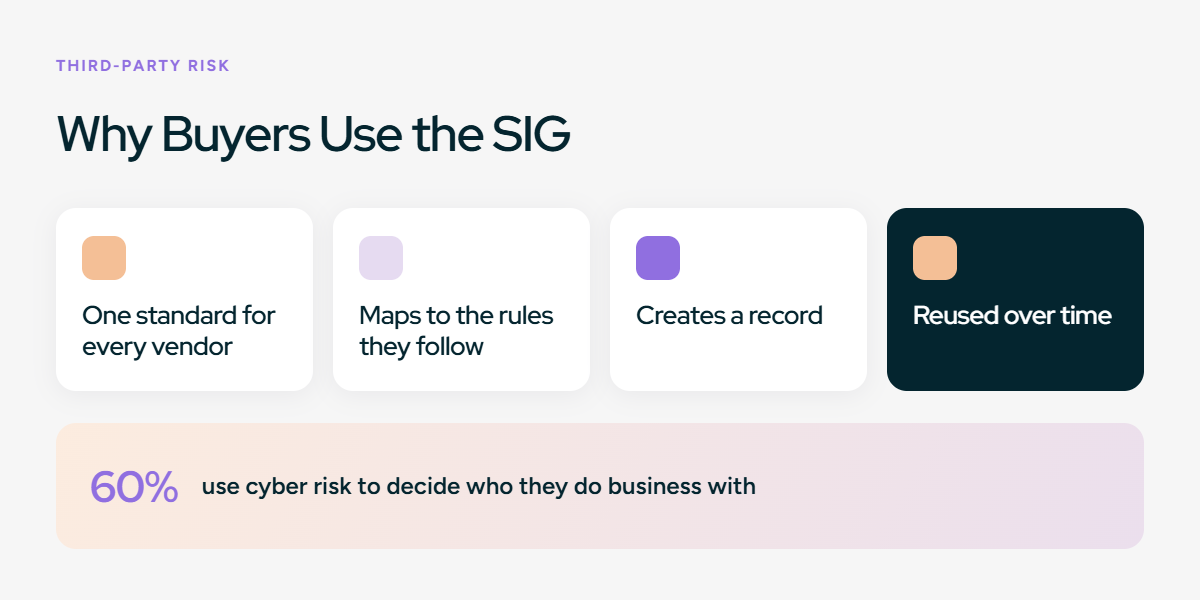
When you handle a buyer's data, their security depends partly on yours. If you get breached, their customer data is exposed too, along with the fines and reputational damage that follow. A buyer sends you a SIG to check your security controls before they take that risk. Gartner projects that by 2025, 60% of organizations will use cybersecurity risk as a primary factor in deciding who they do business with, so for most enterprise deals, completing a SIG is a requirement before they will sign.
Buyers choose the SIG over writing their own questionnaire for four reasons:
- One standard for every vendor. A buyer checking 200 vendors can't compare 200 different questionnaires. The SIG asks every vendor the same questions, so the buyer can score vendors the same way and compare them fairly.
- It maps to the rules they follow. SIG questions are linked to SOC 2, ISO 27001:2022, PCI DSS v4.0, NIST, GDPR, and HIPAA. When you complete a SIG, the buyer can show an auditor that a specific control was checked, without doing that mapping themselves.
- It creates a record. Regulators and boards want proof that a company checked its vendors. A completed, dated SIG is that proof.
- They reuse it over time. The buyer sends the same SIG at onboarding, at annual review, and after a big change, such as you adding a new subprocessor, so they don't rebuild the assessment each time.
Who responds to a SIG questionnaire?
A SIG rarely has a single owner. Answering one well usually involves:
- Security and IT teams for technical controls, architecture, and incident response.
- Compliance, risk, and legal for certifications, policies, and breach obligations.
- Proposal or pre-sales teams to coordinate the response and manage the deadline.
- Sales or account owners for the deal context and urgency.
How to complete a SIG questionnaire
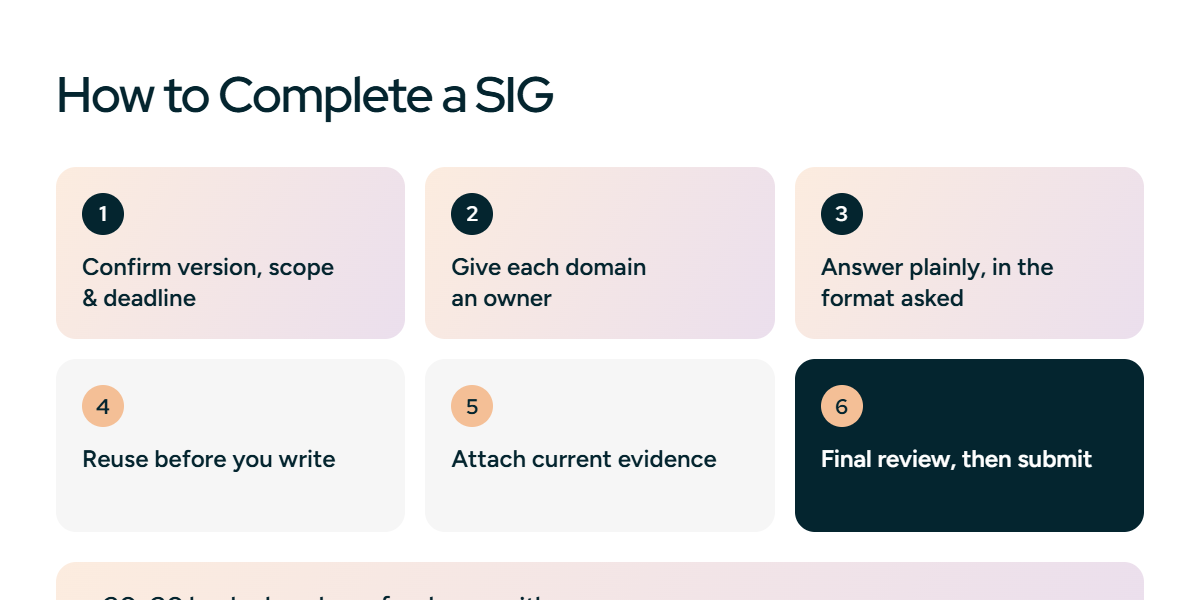
A SIG Core has around 855 questions across 21 domains and needs input from security, compliance, and legal, so treat it as a team task with clear owners. Work through it in this order.
- Confirm the version, scope, and deadline first. Check whether you received SIG Lite, SIG Core, or a custom set, which domains are included, what evidence the buyer wants (policies, SOC 2 report, pen test summary), and when it's due. Answering the wrong scope wastes more time than any other mistake.
- Give each domain an owner. Split the 21 domains by team: access, network, and application security to IT and security; privacy and compliance to legal and GRC; business continuity to operations. Give each owner their questions and a due date. One person can't answer a SIG Core accurately, and unassigned domains are where deadlines slip.
- Answer plainly, in the format the question asks. Most SIG questions want a yes/no or a short factual answer plus proof. State the control simply ("MFA is required for all remote and admin access"), then point to the document that proves it. Don't write a paragraph where a yes and a policy link is what's being scored.
- Reuse before you write. Most SIG questions repeat from one buyer to the next. Take the approved answer from your last SIG or answer library, confirm it's still true, and move on. Send only new or buyer-specific questions to an expert.
- Attach current evidence and check the dates. A correct answer with an expired SOC 2 report or an old policy looks like a problem. Before you submit, make sure every certificate, report, and number you attach is the latest version.
- Do one final review, then submit. Have one person read the whole response to catch answers that contradict each other, confirm evidence is attached where required, and check the wording is consistent. Then submit, and save the final version to your library so the next SIG starts from it.
How long it takes: completing a SIG Core by hand is usually 20 to 30 hours of work across teams. With a maintained answer library, or software that reuses your past answers, it drops to a few hours, most of it reviewing rather than writing.
Best practices for responding to a SIG questionnaire
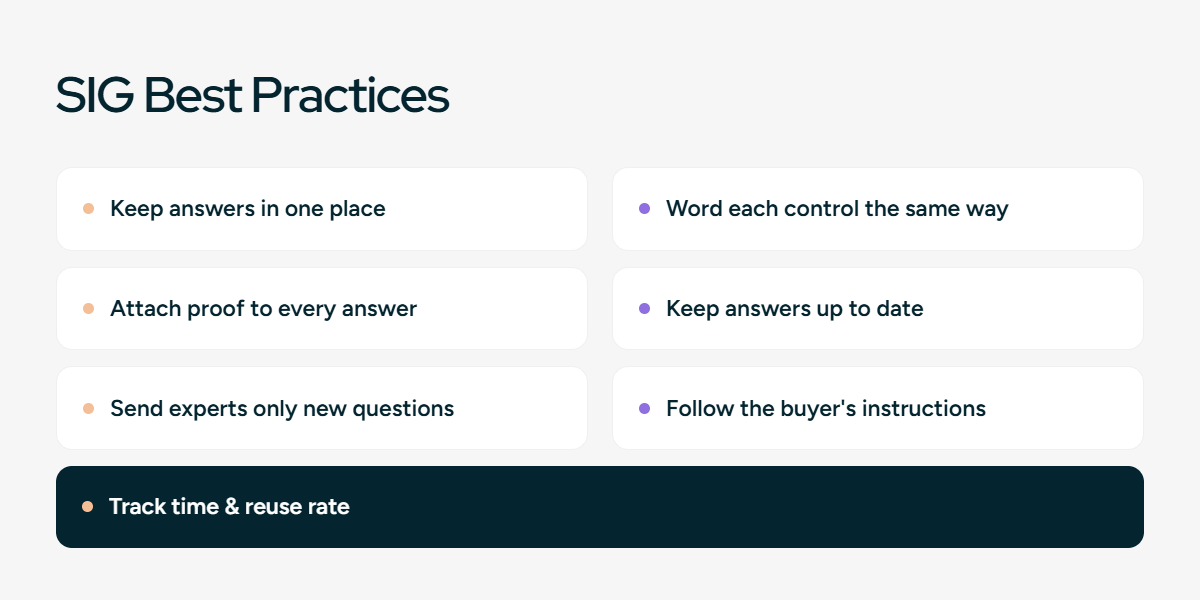
These practices help your SIG clear review the first time, instead of coming back with follow-up questions.
- Keep all your answers in one place. Store every approved answer, policy, and past SIG in one searchable library, owned by a named person. This matters most: it turns each SIG from a from-scratch job into a reuse-and-review task, and it keeps answers consistent when several people respond.
- Word each control the same way every time. Agree on one approved way to describe each control, such as your encryption or your access model, and reuse it word for word. When the same control is worded differently across domains, a reviewer notices and starts asking questions.
- Attach proof to every answer. For each recurring answer, attach the exact source document: your SOC 2 report, ISO certificate, pen test summary, or DR plan. When a document updates, change it in one place so every future SIG uses the current version.
- Keep your answers up to date. Review your library on a set schedule, quarterly works for most teams, and right away whenever a control, certification, subprocessor, or figure changes. Out-of-date answers are the most common reason a SIG fails, because the buyer's reviewer catches the mismatch, not you.
- Only send experts the new questions. Don't hand a subject-matter expert the whole SIG. Give them the few genuinely new questions, plus the buyer's context and the deadline, so they can answer quickly.
- Follow the buyer's instructions exactly. Complete the version and scope they sent, provide evidence in the format they requested, and never leave a question blank. If something doesn't apply, write "not applicable" and say why. An empty answer looks evasive and triggers a follow-up.
- Track your time and reuse rate. Measure how long each SIG takes and how much came from your library. If time goes up or reuse goes down, your library is going stale.
Common mistakes to avoid
Each mistake below has a quick fix, so you can catch it before a reviewer does.
- Reusing outdated answers. An expired SOC 2 date or a replaced policy makes a buyer doubt the whole response. Fix: verify every date and document is current before you submit.
- Guessing at technical answers. A coordinator's best guess on a control is often wrong in a way a security reviewer catches. Fix: get the domain owner's sign-off before marking a section done.
- Inconsistent terminology. Calling the same control "MFA" in one domain and "two-step login" in another makes a reviewer stop to check if they match. Fix: use one agreed term for each control everywhere.
- Skipping requested evidence. Many questions ask for a document, not just a yes; leaving it out forces the reviewer to email and wait. Fix: attach the proof the question names.
- Leaving questions blank. An empty answer reads as evasive and triggers a follow-up. Fix: mark anything that doesn't apply "not applicable" with a one-line reason.
- Skipping the final read-through. A wrong answer here is a security claim a buyer may hold you to, not a typo. Fix: have one reviewer check the full response for contradictions before submitting.
SIG vs. CAIQ and other security questionnaires
The SIG is one of several standardized questionnaires. Here is how it compares to the two you'll meet most often.
Many buyers accept a completed SIG in place of their own custom questionnaire, which is a large part of why it is worth maintaining ready answers.
Is the SIG questionnaire free?
No. The SIG toolkit is licensed from Shared Assessments, and full access comes with membership or a subscription. As the vendor responding, you usually don't buy it yourself, the buyer sends you the version they want completed. If you assess your own vendors, you would license the toolkit to send SIGs of your own.
SIG 2026: what's new
Shared Assessments updates the SIG every year, so the version you receive changes. The SIG 2026 release keeps the 21 risk domains but deepens two areas that matter to buyers now: AI governance, with new mapping to ISO 42001, and operational resilience, aligned with the Business Resilience Council framework.
It also strengthens supply-chain coverage by asking vendors to map interdependencies for critical downstream dependencies, and adds enhanced NIST SP 800-171 mapping. Because the questionnaire changes yearly, keep your answer library current rather than reusing a response from an older version wholesale.
How AI is changing SIG responses
Manually completing a SIG Core can take 20 to 30 hours across several people. AI is changing that on the response side. Modern tools retrieve answers from your past questionnaires and policies, match each incoming question to an approved answer, normalize wording for consistency, and flag gaps or conflicts for a human to review. The work shifts from writing answers to reviewing and approving them.
Answer SIG questionnaires faster with Inventive AI
The hard part of a SIG isn't knowing your security posture, it's the hundreds of repetitive questions, the multiple teams pulled in, and a review that fails if one answer is stale. Inventive AI is an autonomous AI agent platform that takes the repetitive work off your plate.
Here's how it helps with the problems this guide describes:
- The repetitive questions. It drafts answers by retrieving them from your past questionnaires, policies, and connected systems, so the questions you've answered before are filled in for you, and your team reviews instead of rewrites.
- Consistency across responders. Because every answer comes from one shared source of approved content, your responses stay consistent even when several people contribute.
- Stale or conflicting answers. Content Governance flags outdated or conflicting answers, an expired certification or a changed policy, before you submit.
- A built-in compliance checker. It reviews your answers against the frameworks a SIG maps to, such as SOC 2 and ISO 27001, and flags where a response is missing, weak, or inconsistent with a requirement. You see the gaps while you can still fix them, instead of hearing about them from the buyer's reviewer.
- Accuracy you can check. Each drafted answer carries a source citation and a confidence score, so your reviewer can verify it quickly and the buyer gets the evidence they asked for.